Fintech Risk Management in the U.S. Virgin Islands: How Data, Compliance, and Human Judgment Work Together
Key Takeaways
- Fast decisions are only useful when the underlying data is reliable, secure, and relevant.
- Analytics and automated models should direct attention, not remove accountability.
- Human review is especially important for high-impact, unusual, or disputed decisions.
- Compliance is more effective when it is built into everyday workflows.
- Risk teams should monitor outcomes over time because customer behavior, fraud methods, and operating conditions can change.
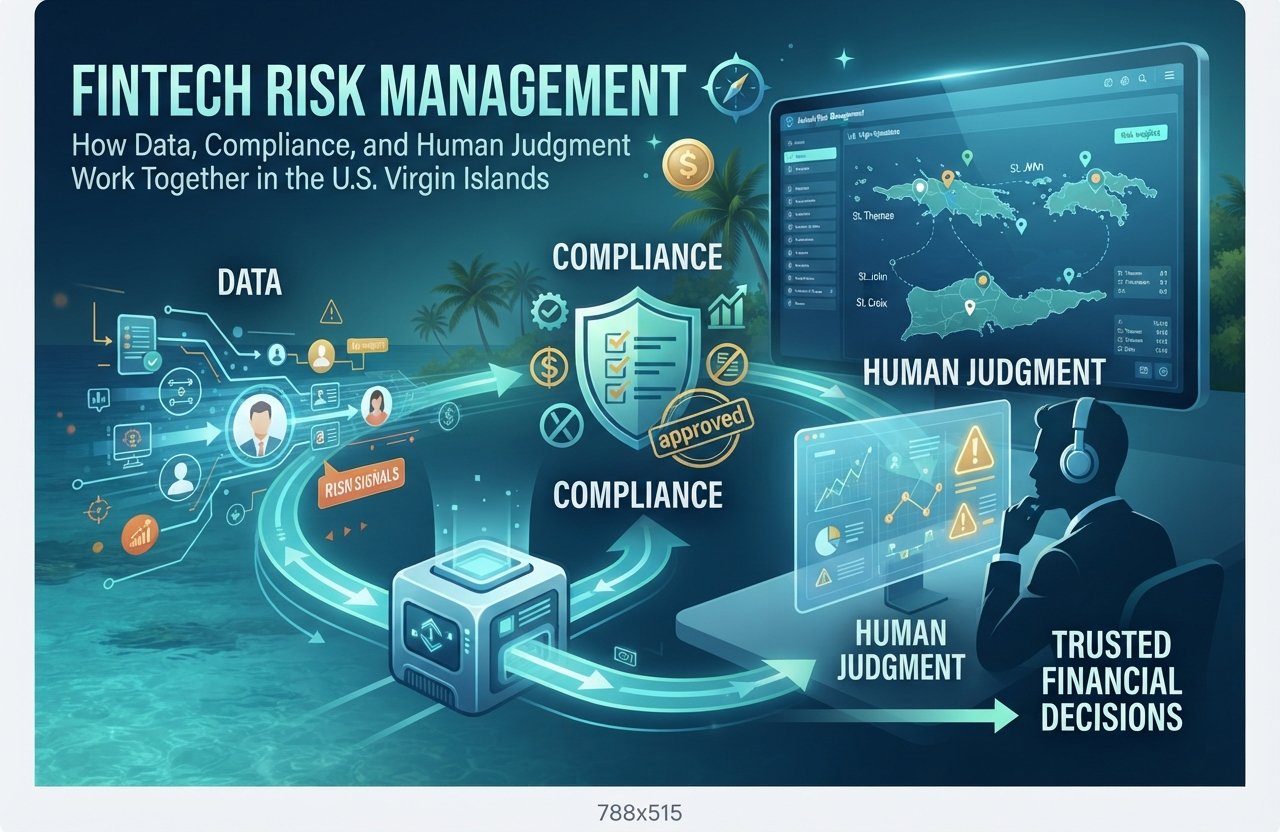
Fintech risk management has a local dimension in the U.S. Virgin Islands, where firms may serve customers, partners, and vendors across island communities and beyond. The business perspective of David Johnson Cane Bay Partners is a useful reminder that sound financial technology operations depend on more than rapid digital decisions alone. They require disciplined data practices, accountable controls, and people who can recognize when an automated result needs a closer look.
In 2026, lenders, payment providers, and financial platforms can process large volumes of applications, transactions, and customer interactions quickly. That speed can improve service, but it can also magnify mistakes when data is weak, controls are unclear, or teams rely on automated tools without sufficient oversight.
Why Fintech Risk Management Looks Different
Digital finance creates a continuous flow of risk signals. A single customer journey can include identity information, device data, payment behavior, support contacts, and repayment activity. Used carefully, these inputs can help teams identify possible fraud, assess creditworthiness, and investigate unusual activity. Used carelessly, they can create inaccurate conclusions, privacy concerns, or inconsistent customer experiences.
Automation is valuable for routine tasks such as sorting alerts, applying consistent rules, and highlighting patterns that would be difficult to spot manually. Still, speed should not replace accountability. Every important system should have a defined purpose, clear ownership, documented limits, and a process for escalation when its recommendation appears questionable.
Start With Reliable and Useful Data
Risk decisions can only be as dependable as the information behind them. Teams should know where each data point came from, how it was collected, how often it changes, and whether it remains appropriate for the decision at hand. Missing records, duplicate accounts, outdated contact details, conflicting income fields, and poorly documented data sources can all distort results.
Core Data Checks
- Confirm the source and permitted use of each important data field.
- Check whether records are current and complete.
- Resolve duplicate, conflicting, or clearly implausible entries.
- Limit access to sensitive information based on job responsibilities.
- Document material changes to data sources, definitions, and validation rules.
For example, a lender might approve applications quickly through an automated workflow. If an income field is routinely incomplete or incorrectly formatted, qualified applicants could be routed to unnecessary manual review. In contrast, higher-risk applicants receive a result that does not reflect their full circumstances.
Use Analytics to Support Better Decisions
Analytics can help risk teams compare application patterns, payment performance, fraud alerts, operational queues, and customer outcomes. The goal is not to let a dashboard make every decision. The goal is to identify where investigation, policy review, or customer support is most needed.
Useful Analytics Questions
- Which patterns are associated with early repayment problems or account losses?
- Are approval rates changing by channel, product, or customer segment?
- Which fraud alerts produce meaningful investigations, and which produce noise?
- Are any rules creating an excessive number of false positives?
- Did outcomes change after a model, vendor, or policy update?
Keep Human Judgment in the Decision Loop
Human review matters when decisions affect access to credit, account services, fraud recovery, or a customer’s ability to resolve a disputed result. Automated systems can recognize patterns at scale, but a trained reviewer can assess context that may not fit neatly into a model.
Meaningful review requires more than asking an employee to click “approve” or “decline.” Reviewers need enough information, sufficient time, and real authority to challenge a recommendation. Practical escalation points include high-value transactions, inconsistent identity details, unusual application behavior, customer disputes, and cases near an approval threshold.
Build Compliance Into Everyday Workflows
Compliance should be part of product design, onboarding, monitoring, customer support, and vendor oversight. A policy is less useful when employees cannot apply it during a real investigation or service issue. Teams considering evidence standards, approvals, investigation records, and escalation responsibilities can benefit from ongoing discussion of financial crime risk in the wider financial services community.
Questions for a Practical Compliance Review
- What decision or risk does this control address?
- Who owns the control and its supporting documentation?
- What evidence indicates that the control operated as intended?
- What happens when a rule produces an unusual or disputed result?
- How quickly can the process be adjusted when risks change?
Make Automated Models Easier to Explain
Model transparency helps internal teams test systems, helps customer-facing teams communicate clearly, and helps leaders understand where automation should stop. A model does not need to disclose every technical detail to be explainable. It should, however, have a documented purpose, known inputs, measurable performance, and understandable reasons for its major recommendations or alerts.
A Basic Model Review Checklist
- Define the model’s intended use and prohibited uses.
- List the data fields and key assumptions involved.
- Test error patterns across relevant customer groups.
- Measure false alerts, missed risks, and operational impact.
- Set boundaries for automatic action and human escalation.
- Document review ownership and retest after a material change.
Manage Vendor and Third-Party Risk
Fintech organizations often depend on outside providers for cloud services, identity verification, payment processing, data tools, fraud detection, and customer support. Each relationship can affect privacy, resilience, customer experience, and the ability to continue operating during an outage. Vendor review should cover data handling, incident reporting, service commitments, control testing, and the plan for ending or replacing the relationship.
Track Results With Clear Risk Metrics
Approval rates and revenue figures alone do not show whether risk controls are working. Teams should monitor fraud loss rate, false-positive rate, manual-review volume, early repayment performance, complaint trends, model error rates, alert-resolution time, and vendor outage hours. Trends across several review periods usually provide more insight than a single strong or weak month.
A Simple Five-Step Risk Management Process
- Map the decision. Identify what the system decides, recommends, or flags.
- Review the data. Check quality, access, relevance, and potential bias.
- Set control points. Define when automation must pause for human review.
- Test outcomes. Measure accuracy, speed, customer impact, complaints, and losses.
- Improve continuously. Update rules, training, models, and documentation as evidence develops.
What Fintech Leaders in the U.S. Virgin Islands Should Plan For Next
Strong risk programs are designed to adapt. Leaders should expect evolving customer needs, new products, changing fraud tactics, vendor changes, and fresh operational pressures. Building smaller feedback loops makes it easier to identify issues before they become larger failures. Discussions of AI-driven compliance systems also reinforce the need to connect explainability, data quality, cybersecurity, and human judgment rather than treating them as separate projects.
Conclusion
Fintech risk management is not a choice between technology and people. Data can reveal patterns, models can accelerate routine work, and compliance can establish clear boundaries. Human judgment provides the context and accountability that high-stakes financial decisions require. When those elements work together, organizations in the U.S. Virgin Islands can pursue efficient digital services without sacrificing control, transparency, or customer trust.